Compliance as a Service: Audit-Ready Without the Panic
No empty claims. Compliance you can prove.
Regulations keep piling up, and it's not enough to say you're compliant. You have to be able to prove it. Most businesses don't have someone dedicated to tracking every requirement, documenting every control, and getting audit-ready before the audit is even scheduled.
Succurri builds that structure for you: policies, continuous monitoring, documentation, and the executive-level guidance to back it all up. Whether you're prepping for HIPAA, NIST, PCI, or whatever framework applies to your business, you'll have something real to show for it when someone asks.
Run Your Audits Like a Drill, Not an Emergency
Know the plan before the auditor walks in.
Think of a compliance audit as the drill and a breach as the real emergency. The whole point of practicing is so nobody's scrambling when it actually counts. But most businesses skip the practice: policies get written the week before an audit, documentation is scattered across three different people's inboxes, and nobody's quite sure who's supposed to do what if something actually goes wrong.
Succurri builds the plan ahead of time, with ongoing oversight, structured processes, and documentation that's ready before anyone asks for it, so your team walks into every audit already knowing the drill and isn't caught flat-footed if a real emergency ever hits.
The Work:
The unglamorous stuff that makes audits boring instead of terrifying.
The Rewards:
What you actually get done for doing the work ahead of time.
Together, that's compliance you can prove on command, whether it's an auditor, an insurer, or a client asking.
We Speak Auditor Fluently
Documentation that actually holds up when someone asks for it, that's the real test. Plenty of firms can write a policy. Fewer can walk you into an audit, an insurance review, or a client security questionnaire already prepared, with evidence organized and controls validated ahead of time.
Our compliance consultants, IT leaders, and security specialists build programs that survive that moment, not just look good sitting in a folder.
REAL RESULTS
Proof That What We Do Isn't Just Paperwork
Compliance sounds abstract until it's your audit, your insurer, or your vendor risk on the line. Here's what it actually looked like for three businesses in three very different situations, and the outcomes after we got involved.
The Healthcare Org That Needed HIPPA, Not Just a Binder
A healthcare provider needed real documentation and clear policies to actually meet HIPAA requirements, not just check a box. We built out their policies, ran risk assessments, and put continuous monitoring in place. Result: stronger compliance readiness, lower risk, and a clean pass during external review.
The Financial Firm Drowning in Scattered Paperwork
A financial services company had compliance documentation spread across systems with no clear process behind it. We centralized everything, set real governance standards, and stayed on as ongoing oversight. Result: a 70 percent reduction in audit prep time, clearer visibility for leadership, and stronger trust with their clients.
The Manufacturer Who Didn't Know What Their Vendors Were Doing
A manufacturing firm had third-party tools and integrations nobody was really keeping an eye on. We evaluated their vendors, updated contracts, and put monitoring in place. Result: lower vendor risk, better documentation, and closer alignment with industry standards.
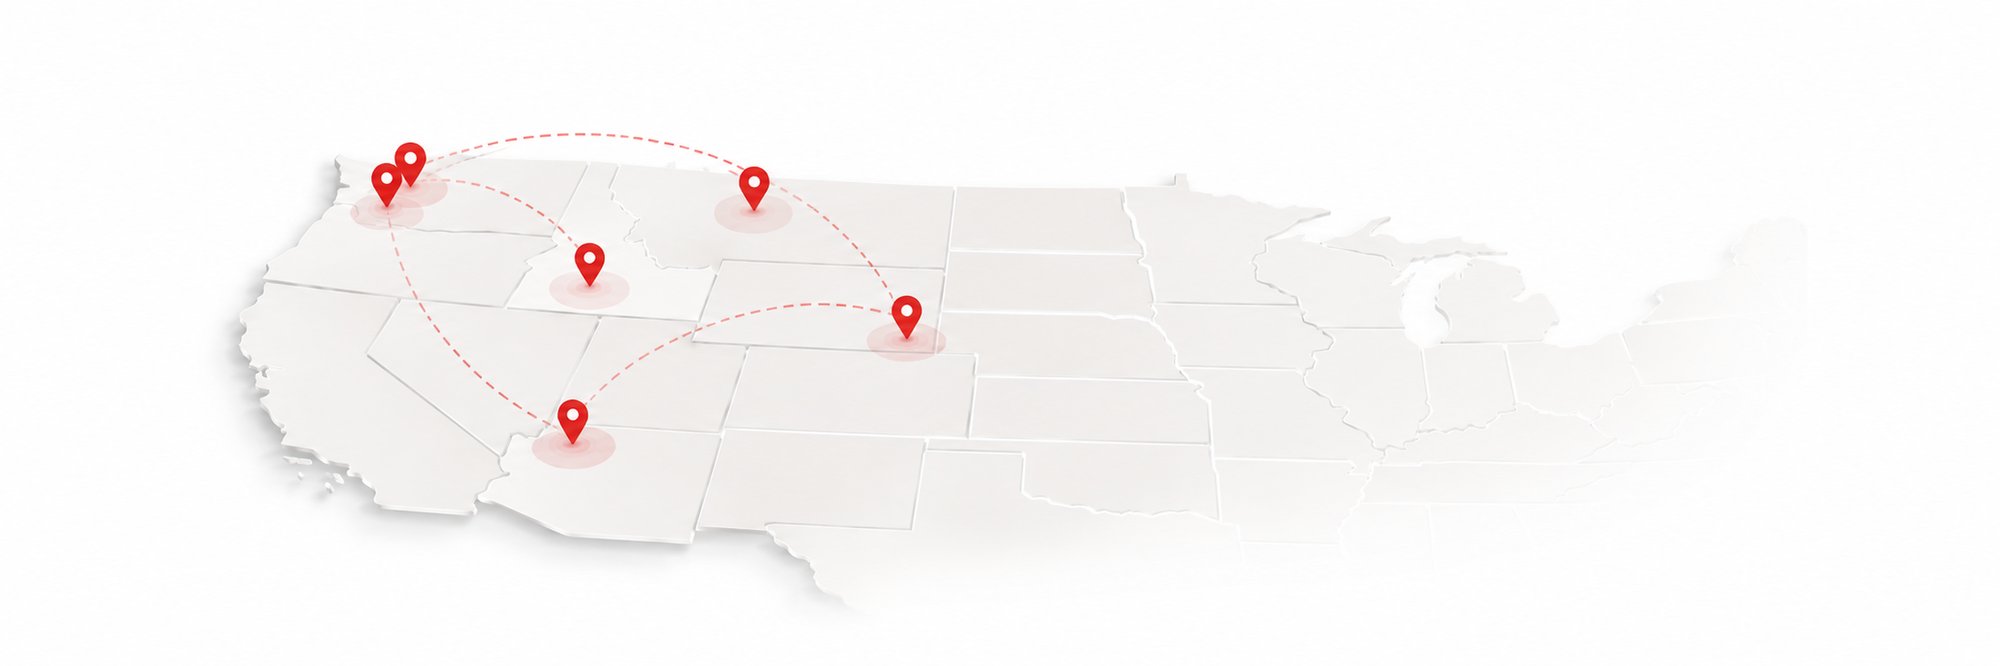
OUR LOCATIONS
Areas We Serve

Stop Guessing Whether You're Compliant. Prove It.
If documentation, unclear requirements, or audit season have you on edge, Succurri can help. We build compliance programs that hold up under scrutiny and scale as your business grows.
Ready to talk? Reach out through our contact page.
FAQs
Frequently Asked Questions About Compliance as a Service
-
What is compliance as a service (CaaS)?
It's ongoing compliance management instead of a one-time project. Succurri handles framework mapping, policy development, risk assessments, and continuous monitoring so your organization stays audit-ready year-round instead of scrambling when a deadline hits.
-
Which compliance frameworks do you support?
It depends on your industry and requirements. We work with frameworks like HIPAA, NIST, CIS, and PCI, along with internal governance standards, and we help you identify which ones actually apply to your business before mapping your environment against them.
-
How is this different from just writing a compliance policy?
Plenty of firms can write a policy. Fewer can walk you into an audit, an insurance review, or a client security questionnaire already prepared, with evidence organized and controls validated ahead of time. That's the difference between paperwork and a program that holds up.
-
Do you help with audits and insurance reviews?
Yes. We prepare documentation, validate controls, and get your organization ready before an audit or insurance review starts, so you're walking in with evidence in hand instead of pulling records together under pressure.
-
What size businesses do you work with?
Most of our compliance clients are small and mid-sized businesses that need real oversight but don't have the internal resources to manage frameworks, documentation, and audits on their own. We scale the program to fit your business rather than handing you a one-size-fits-all package.
Your Compliance Questions, Answered by a Person
Whether it's an upcoming audit, an insurance review, or just uncertainty about where you stand, call the office nearest you and talk to a real person, not a script.
-
Everett Office - Open 8 AM - 5 PM 206-340-1616
-
Mesa Office - Open 8 AM - 5 PM 480-795-2181
-
Kalispell Office - Open 8 AM - 5 PM 406-730-5105